OPEN TO WORK · SECURITY ENGINEERING

Mahmoud Ouf

Application Security & Offensive Security Engineer | B.Sc. Software Engineering

Living after 0x7c00

Recognition

SECURITY FINDINGS & RECOGNITION

DigitalOcean Critical

Responsible Disclosure — Critical Vulnerability

Validated critical vulnerability reported through DigitalOcean’s authorized bug bounty program and acknowledged in Bug Bounty Hall of Fame.

April 2019 · Bug Bounty · Responsible Disclosure · Bug Bounty Hall of Fame

View Bugcrowd profile ↗
Pinterest Bug Bounty Hall of Fame

Responsible Disclosure — Security Vulnerability

Validated security finding responsibly disclosed via Pinterest’s bug bounty program and acknowledged in Bug Bounty Hall of Fame.

June 2018 · Bug Bounty · Responsible Disclosure · Bug Bounty Hall of Fame

View Bugcrowd profile ↗
Dell Bug Bounty Hall of Fame

Responsible Disclosure — Security Finding

Validated security finding submitted through Dell’s official bug bounty program and acknowledged in Bug Bounty Hall of Fame.

April 2018 · Bug Bounty · Responsible Disclosure · Bug Bounty Hall of Fame

View Bugcrowd profile ↗

20+ aggregate acknowledgments across Bugcrowd — View Bugcrowd profile ↗

References & Verifiable Assessment Logs Available Upon Request

HR & ATS · Verified

Credentials

Certified · 2026

Certified Network Security Practitioner (CNSP)

The SecOps Group — 2026

with Merit · ID 11896945

View Credential
Certified · 2023

Blue Team Junior Analyst

SecurityBlue Team — 2023

Blue-team operations & incident response fundamentals

View Credential
Certified · 2023

Cyber Threat Intelligence

IBM — 2023

Threat analysis & intelligence gathering

View badge
Certified · 2024

Jr Penetration Tester

TryHackMe — 2024

Penetration testing methodologies & techniques

Verify

Education · Verified

B.Sc. Software Engineering

Tomsk State University — Conferred Jul 2026

Sep 2022 – Jul 2026

Software engineering foundations — system reasoning, architecture & documentation that makes findings reproducible.

Core tool stack

  • Burp Suite
  • Nmap
  • Python
  • BloodHound
  • Wireshark
  • ELK / SIEM
  • Impacket
  • Bash
  • Linux
  • Windows
  • AD / Kerberos
  • Docker
  • Git
  • SQLMap
  • Nuclei
  • ffuf
  • Ghidra (lab)
  • Metasploit (lab)
  • Sigma
  • Splunk (lab)
  • Suricata (lab)
  • YARA (lab)
  • MITRE ATT&CK
  • Incident Response
  • Cloud Security (AWS IAM)

Research

SECURITY RESEARCH and Writeups

Experience

Software Engineer, Intern

Context: University research projects requiring software implementation and academic-grade documentation.

Responsibilities:

  • Designed and developed 2 MVPs within defined research scope
  • Created 12 diagrams (UML, component and activity) to visualize system structure and interactions
  • Produced technical documentation aligned with academic standards
  • Participated in the full software development lifecycle — requirements, design, implementation, documentation

Outcomes:

  • Delivered 2 MVPs with complete documentation packages
  • Provided 12 diagrams supporting review and handover
  • Met publication-ready documentation standards

Engineering work that builds system reasoning, architecture and tooling — not security assessment.

July 10 – September 10, 2024 Bastion Security

Security Engineering Intern

Completed Penetration Testing & Application Security internship track: company-led lectures, CTF challenges, vulnerability-exploitation lab work.

  • Conducted a research project analyzing web application cache-attack techniques.
  • Ranked Top 5 of 100 in internal penetration-testing and privilege-escalation challenges.

View Credential →

The path

EVERYTHING ABOUT ME

View
Pentesting Networking Sysadmin Tools Scripting Projects Concepts Awards Experience Education Courses Certificates Blogs

Context

About Me

A practical security perspective shaped by both testing and operating real systems.

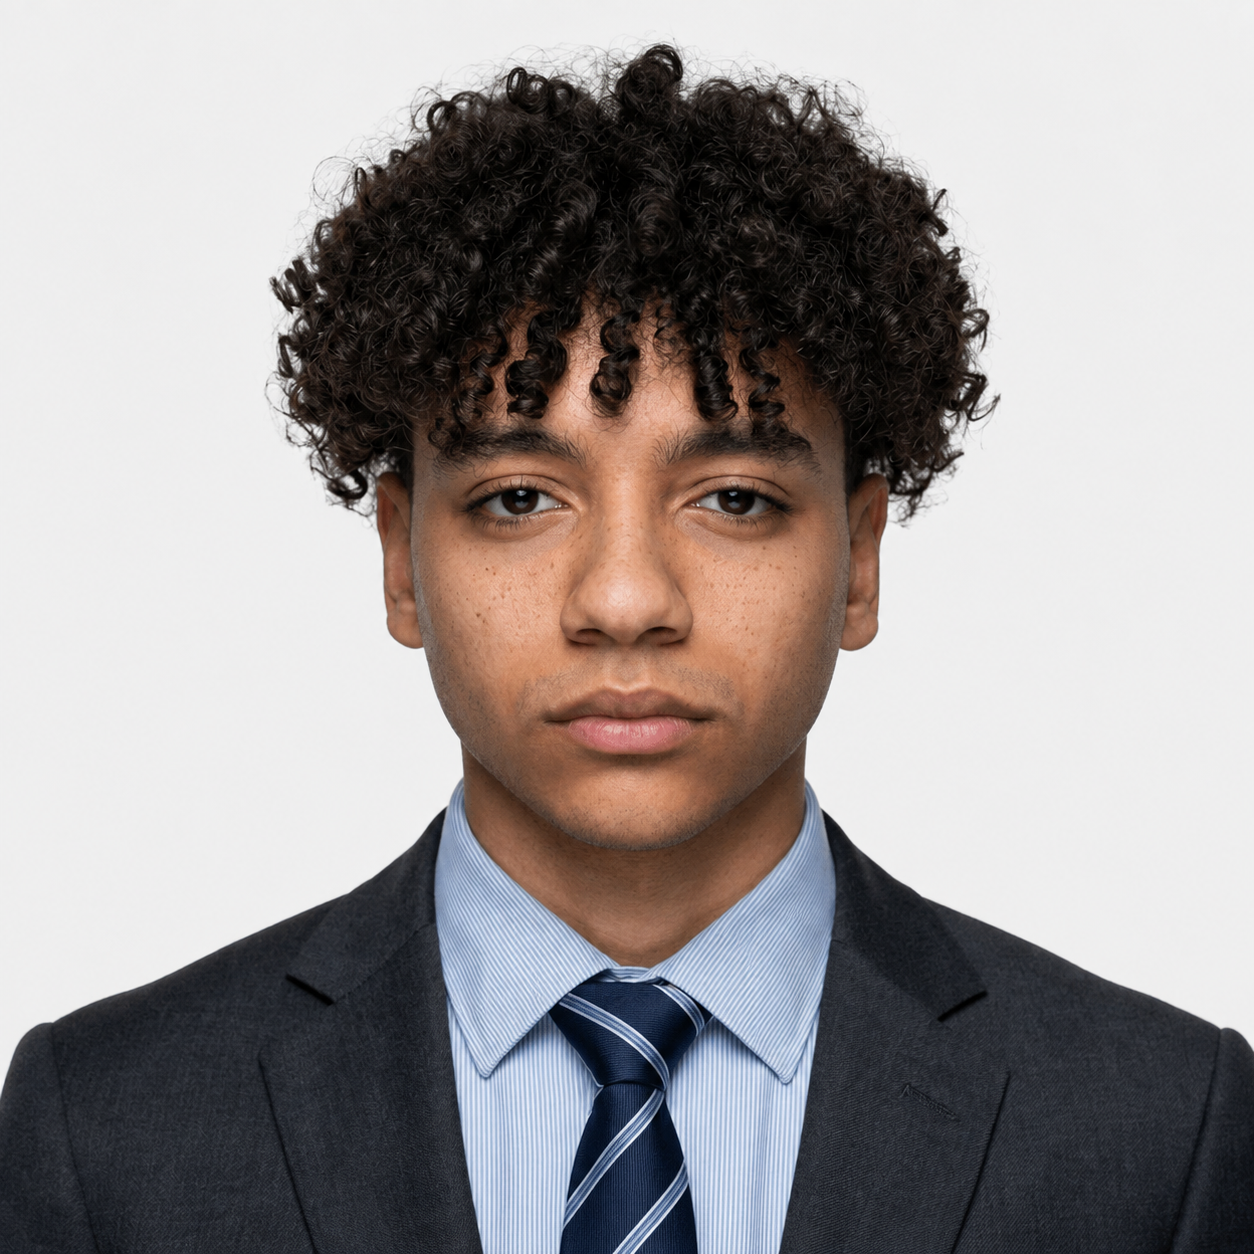
Mahmoud Ouf working across cybersecurity and systems engineering
Security engineering with an operator's mindset.

Driven by a deep fascination with low-level mechanics, I view cybersecurity not just as code, but as a craft. Software Engineer by degree, Offensive Security researcher by practice, I specialize in bridging application code quality with web/API penetration testing, threat modeling, and secure architecture.

My background in Software Engineering from Tomsk State University fuels my systematic approach to architecture, documentation, and automated tooling. On the offensive side, I conduct authorized security assessments and uncover critical vulnerabilities—with named disclosures for Verisign, DigitalOcean, Pinterest, and Dell, 20+ Bugcrowd acknowledgments, a Top 5 placement in Bastion’s CTF, and published research.

I test strictly within authorized scope, practice responsible disclosure, and align assessments with frameworks like OWASP ASVS, NIST CSF, ISO 27001, and GDPR guidelines to build fundamentally resilient systems.
16 notes in archive — Browse all →

Capabilities

Detailed Skills Matrix

Evidence-tiered and honestly scoped — Core · Applied · Familiar · Engineering — strongest to exposure, no percentage scores.

CORE

Hands-on in labs and authorized assessments — regularly practiced, including reporting

  • Web/API Security
  • Vulnerability Assessment
  • Linux
  • Windows
  • TCP/IP
  • Privilege Escalation (lab)
  • Burp Suite
  • Nmap
  • Python
  • Bash

APPLIED

Applied in internships and labs — developing depth

  • OWASP
  • Network Security
  • Active Directory
  • Kerberos
  • Wireshark
  • BloodHound
  • Impacket
  • Docker
  • System Administration
  • Firewall
  • SIEM (ELK)
  • Incident Response
  • MITRE ATT&CK
  • Cloud Security (AWS IAM)

FAMILIAR

Exposure / lab — currently developing, not a primary strength

  • Ghidra (lab)
  • Metasploit (lab)
  • Cobalt Strike (exposure)
  • Sliver (lab)
  • Nuclei (lab)
  • SQLMap (lab)
  • ffuf (lab)
  • Malware Analysis (lab)
  • Threat Intelligence (exposure)
  • Exploit Development (lab)
  • Red Team (lab)
  • YARA (lab)
  • Sigma (lab)
  • Suricata (lab)
  • Splunk (lab)

ENGINEERING

Programming, systems and professional effectiveness — supports testing and tooling

  • JavaScript
  • C/C++
  • Assembly
  • SQL
  • Git
  • Presentation Skills
  • Problem Solving

Tiers reflect hands-on evidence: Core = regularly practiced with reporting · Applied = internship/lab depth · Familiar = lab exposure · Engineering = systems & professional effectiveness.

Next conversation

Let's talk about security.

Open to application security, offensive security, security engineering, and infrastructure-security roles — worldwide (remote & on-site).