 Open note
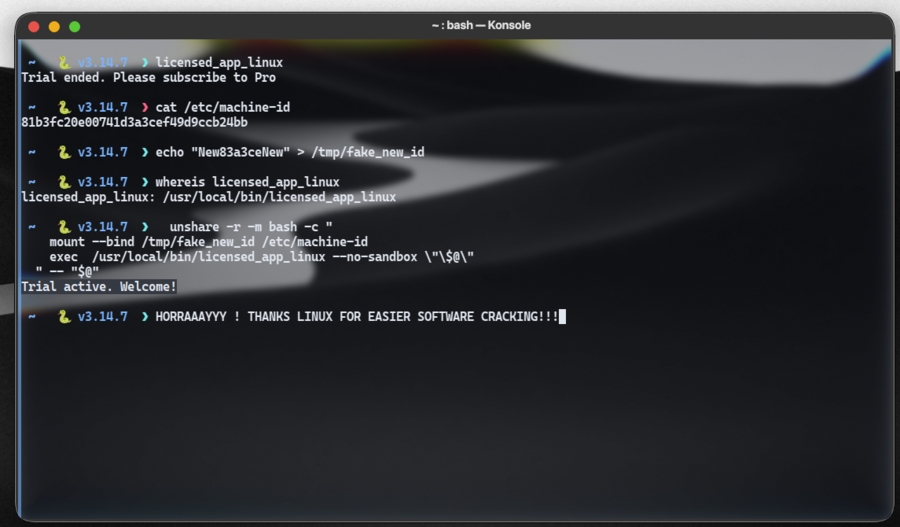
Linux Third-Party Desktop Software Trial Bypass Vulnerability
Controlled lab simulation of real-world Linux desktop trial checks that trust /etc/machine-id — isolated bypass via unshare & mount --bind, detection with strings/strace, and server-side hardening.